As of 29 August 2026, OpenAI's website hosts an open call for collective action on cyber defense. It is supported by a broad group of organizations from technology, security, financial services, telecommunications and consulting. Its central idea is straightforward: artificial-intelligence capabilities are developing on both sides, and defenders have a limited window in which to remove weaknesses that have been known for years.
The letter is not the announcement of a new security product, nor is it evidence that every attack already uses artificial intelligence. It is a forecast and recommendation from its signatories. For the leadership of an ordinary company, another point matters more: even advanced tools will not help if the company does not know which systems it operates, who has privileged access, which devices are out of support and whether it can recover after an incident.
What OpenAI and the signatories actually propose
The call names three principles. It argues that the security status quo will not be enough because organizations carry longstanding bugs, excessive permissions, misconfigurations, unpatched software, weak authentication and technical debt. More defenders should gain access to tools capable of supporting cyber defense. Practical knowledge, verified fixes, threat intelligence and response playbooks should also be shared.
For organizations, the call recommends making defense a leadership priority, fixing the highest-risk weaknesses, verifying the result without endangering essential operations and raising the security bar for what a company buys, builds and deploys — including AI-generated code. It emphasizes least privilege, strong access control, defense in depth and verified compensating controls where an immediate patch is not possible.
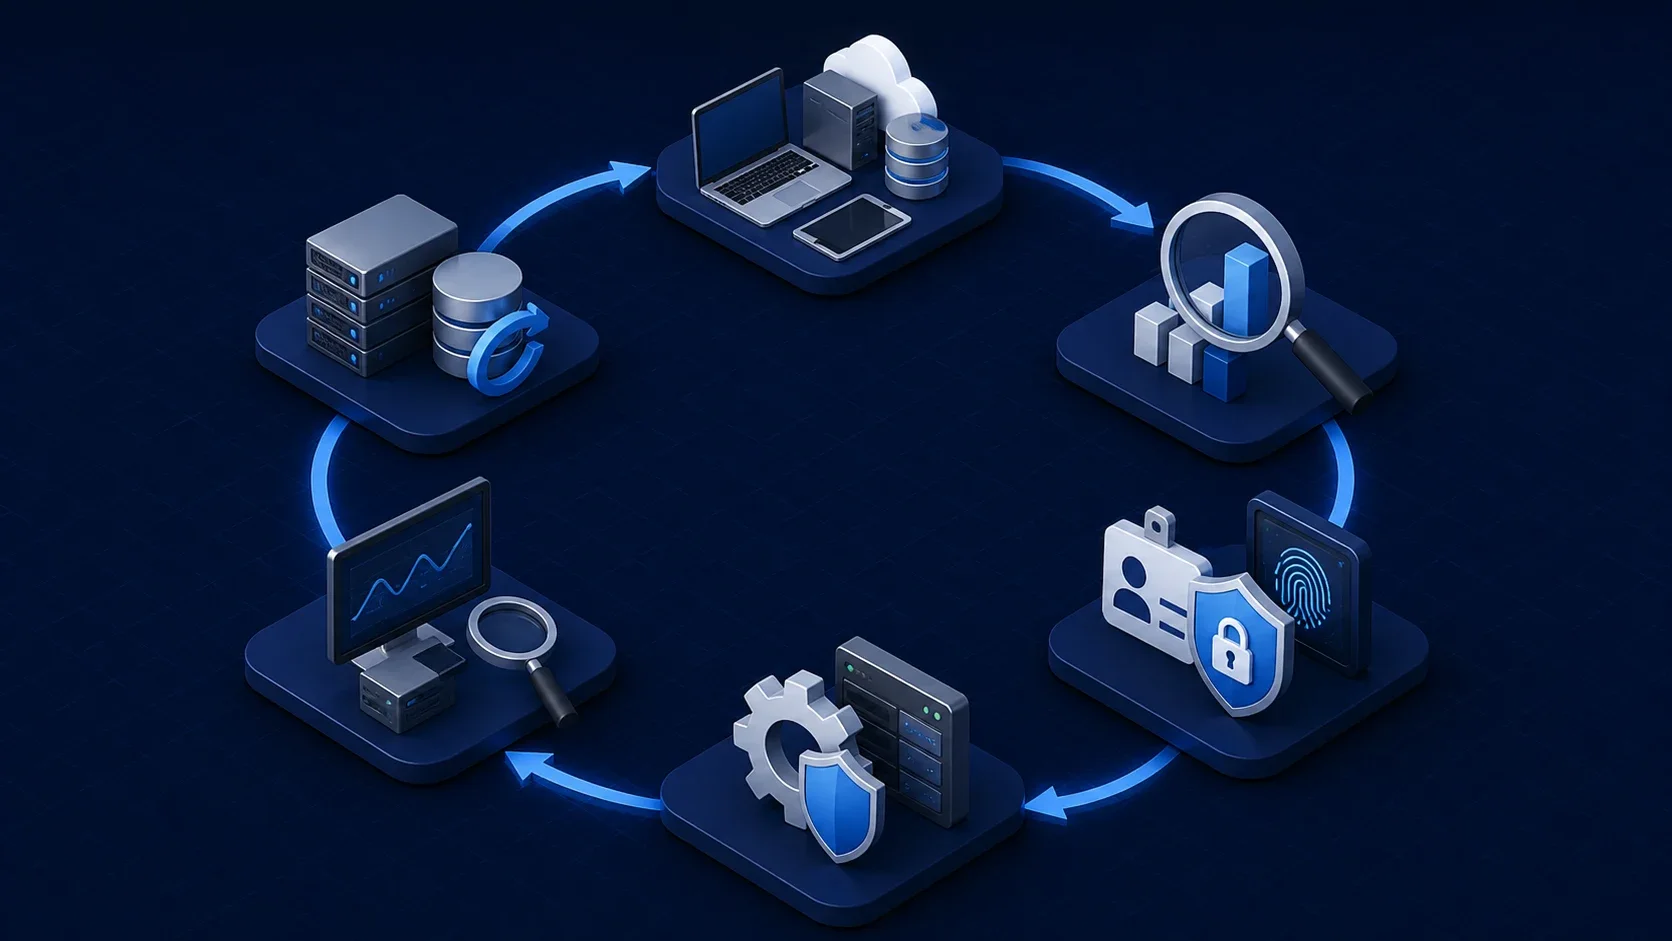
This direction is consistent with the NIST Cybersecurity Framework 2.0. The framework is intended for organizations regardless of size or sector and organizes cybersecurity around govern, identify, protect, detect, respond and recover. NIST also stresses that the framework does not prescribe one technical recipe. Each organization must adapt the outcomes to its own risks, resources and operational priorities.
What collective defense means for an ordinary company
Collective defense does not mean transferring responsibility to a supplier or waiting for someone to send a universal fix. It means preparing the environment so that a company can receive trustworthy information, assess it, apply it and verify it quickly. If a vendor warns about a firewall flaw, the internal team or administrator must know where that model is used, which operations it protects, who may approve a change and how to roll the configuration back if an update causes an outage.
Practical collaboration therefore includes clear contacts for the IT provider, internet carrier, cloud partner and suppliers of critical applications. Equally important are rules that turn a vulnerability notice into a task with an owner, deadline, test and evidence of completion. A shared threat list without inventory and accountability merely creates more email.
For a smaller company, professional network administration and monitoring can also provide a collective element: the provider follows device support, relevant security advisories and configuration changes across multiple environments, while carrying out a concrete intervention only within an authorized scope and with the client's operations in mind.
Six steps that can be implemented now
- Build an inventory with ownership and business relevance. A notebook list is not enough. Include identities, servers, cloud services, network devices, remote access, backups, applications, integrations and suppliers. Name an owner and the impact of an outage for every item.
- Prioritize by risk and operations. Weaknesses that are realistically exploitable, internet-facing, connected to a privileged account or able to interrupt an essential service deserve the highest priority. A severity score without company context is not enough.
- Restrict access. Review administrator accounts, enable appropriate multi-factor authentication, separate everyday and privileged identities, remove unused accounts and review permissions regularly. This is a foundation for managed cybersecurity, not a one-time setting.
- Patch with a test and rollback plan. A security update needs an owner, maintenance window, configuration backup, test of essential functions and a rollback procedure. If a system cannot be fixed immediately, the temporary control must be specific, time-limited and verified.
- Collect useful logs and verify the outcome. Monitor privileged sign-ins, account and configuration changes, endpoint protection status, critical errors, backups and unexpected communication. After remediation, verify that the vulnerable version or exposed access path has actually disappeared.
- Prepare response and recovery. Decide who may isolate a device, who authorizes downtime, how suppliers are contacted and from which source data will be restored. Test backups regularly and run at least a tabletop exercise for an outage of a key service.
Collective defense works only when external information ends in a verified change in your own environment — not merely in a forwarded alert.
How to use AI safely in defense
AI can help triage findings, explain configurations, review code, propose detection rules or accelerate preparation of a fix. Its output is not proof of correctness. A security team must know the source of the data, validate the proposal against the system and keep a human in the decision loop whenever production, permissions or incident response may change.
When expanding its Daybreak program on 10 August 2026, OpenAI described specific boundaries for access to advanced cyber models. The program is for approved individuals and organizations performing authorized work; access is tied to identity verification, account security, monitoring, approved-use restrictions and legal attestations. OpenAI also recommends isolated environments, monitoring agent actions and defining the exact scope of authorized systems.
This is not a universal manual for every AI tool, but it is a useful security pattern. Before using AI, a company should define approved use cases, input-data classification, approved accounts and services, output retention, the review method and the audit trail. Sensitive logs, personal data, passwords, private keys and production configurations do not belong in an unapproved consumer tool.
The NIST AI Risk Management Framework recommends managing AI risks throughout the design, use and evaluation of a system. In security practice, this means measuring not only speed but also false positives, missed risks, fix quality, adherence to scope and the ability to explain afterwards who approved a recommendation.
What company leadership should monitor
Leaders do not need to review every technical alert. They do need to see whether the organization can turn risks into decisions and results. A monthly or quarterly overview can include the share of critical assets with an owner, out-of-support systems, time to remediate the highest risks, coverage of privileged accounts with strong authentication, successful recovery tests, unresolved exceptions and the status of incident-response exercises.
Supplier dependency also matters. For every essential service, it should be clear who provides an alert, who prepares remediation, who authorizes it and which logs or evidence the company receives. Without these answers, an organization may own more tools but still be unable to show that it is safer after a fix.
When expert help makes sense
External assistance is proportionate when the company lacks a complete inventory, cannot separate essential services, uses out-of-support equipment, has no centralized logs or fears an outage during an update. Properly structured IT outsourcing should combine operational knowledge with a security plan, not replace leadership decisions.
A suitable first step is an authorized review of assets, identities, remote access, firewall rules, updates, backups, logging and supplier dependencies. Its output should be a short prioritized plan: what to fix now, what to restrict temporarily, what to replace, who owns each task and how the outcome will be verified. That is how a global call becomes practical defense for one company.
Sources and further information
- A call for collective action on cyber defense — OpenAI
- Expanding Daybreak as the Cyber Defense Window Narrows — OpenAI
- The NIST Cybersecurity Framework (CSF) 2.0 — National Institute of Standards and Technology
- AI Risk Management Framework — National Institute of Standards and Technology